Vulnerability discovery is the continuous process of identifying, validating, and assessing weaknesses across an organization's endpoints and servers. It's for enterprise security teams, critical infrastructure operators, manufacturers, and government contractors managing mixed Windows, Linux, physical, virtual, IT, and OT environments.
Without it, remediation prioritization is guesswork. You can't patch what you don't know exists, and you can't prove continuous monitoring to an auditor or a contracting officer without evidence.
Discovery gets mentioned in the same breath as scanning, patching, penetration testing, EDR, and SIEM, but its actual workflow and limits are frequently misunderstood. This guide breaks down what discovery is, how it works end to end, what affects its accuracy, and when periodic assessment isn't enough.
Key Takeaways
- Discovery combines inventory, telemetry, correlation, validation, and risk context, not just scanning.
- Coverage must reach endpoints, servers, VMs, OS and package data, ports, permissions, and unmanaged assets.
- Severity alone does not set priority; exposure, exploitability, criticality, and active exploitation do.
- Continuous discovery closes gaps from new assets, configuration drift, and newly disclosed CVEs.
What Is Vulnerability Discovery Across Enterprise Endpoints and Servers—and Why Is It Used?
Vulnerability discovery is the structured identification and validation of weaknesses that could allow unauthorized access, privilege escalation, data exposure, code execution, disruption, or lateral movement. The goal is reliable, actionable findings tied to specific assets, software versions, configurations, users, permissions, and business context, not a bare inventory of CVE numbers.
It's easy to conflate discovery with three related activities, but they're not interchangeable:
- Vulnerability scanning searches for indicators of known weaknesses. Discovery is the broader collection, analysis, validation, and contextualization process that scanning feeds into.
- Vulnerability management adds prioritization, ownership, remediation, exception handling, and reporting after findings exist.
- Penetration testing is a controlled, scenario-based assessment at a point in time. Continuous discovery provides broader, recurring visibility across the whole environment.
Why Endpoints and Servers Need Different Lenses
Endpoints expose user applications, local privileges, and removable-device pathways. Servers host critical services, databases, authentication systems, and operational workloads. A missing patch on a laptop and the same CVE on a domain controller carry very different weight.
Mixed Windows and Linux estates add complexity on top of that: different package managers, patch cadences, service architectures, permission models, and configuration file formats mean a single assessment method rarely covers both well.
Why Organizations Invest in This
- Surface unknown, unmanaged, duplicated, or stale assets before they become permanent blind spots
- Connect CVEs and misconfigurations to the exact host, package, or service requiring action
- Support risk-based remediation instead of treating every scanner alert as equally urgent
- Generate evidence for CMMC, NIST SP 800-series controls, HIPAA, and SOX obligations
Exploitation pressure is also rising. Verizon's 2025 DBIR found exploitation accounted for 20% of initial-access breach vectors, a 34% jump over the prior report.
The same report measured a five-day median from CVE publication to a vulnerability landing on CISA's Known Exploited Vulnerabilities catalog for the scanned cohort. Attackers aren't waiting for your next quarterly scan window.
How Vulnerability Discovery Works Across Endpoints and Servers
Discovery isn't a single scan event. It's a recurring loop:
- Discover assets
- Collect evidence
- Identify weaknesses
- Validate findings
- Prioritize risk
- Remediate
- Verify
- Reassess

Build a Complete Asset Inventory
Start with everything: endpoints, physical servers, VMs, cloud-connected hosts, exposed services, and assets that are offline or intermittently connected. Record ownership, network segment, business function, criticality, and whether each asset supports IT, OT, or both.
Unauthorized, duplicate, or unknown assets don't just slow things down. They create actual discovery gaps and skew risk calculations, since a host nobody's tracking is a host nobody's patching.
Collect Endpoint and Server Telemetry
Gather OS versions, installed applications, package versions, patch state, running services, open ports, accounts, groups, permissions, and configuration data.
The collection method matters. Manual data entry introduces lag and gaps. Automated collection should preserve enough context to distinguish an installed component from one that's actually running and exposed.
Windows and Linux sources differ meaningfully:
- Windows: registry values, installed-service data, and WMI-based attributes
- Linux: package managers, running processes, systemd services, and permission structures across distributions
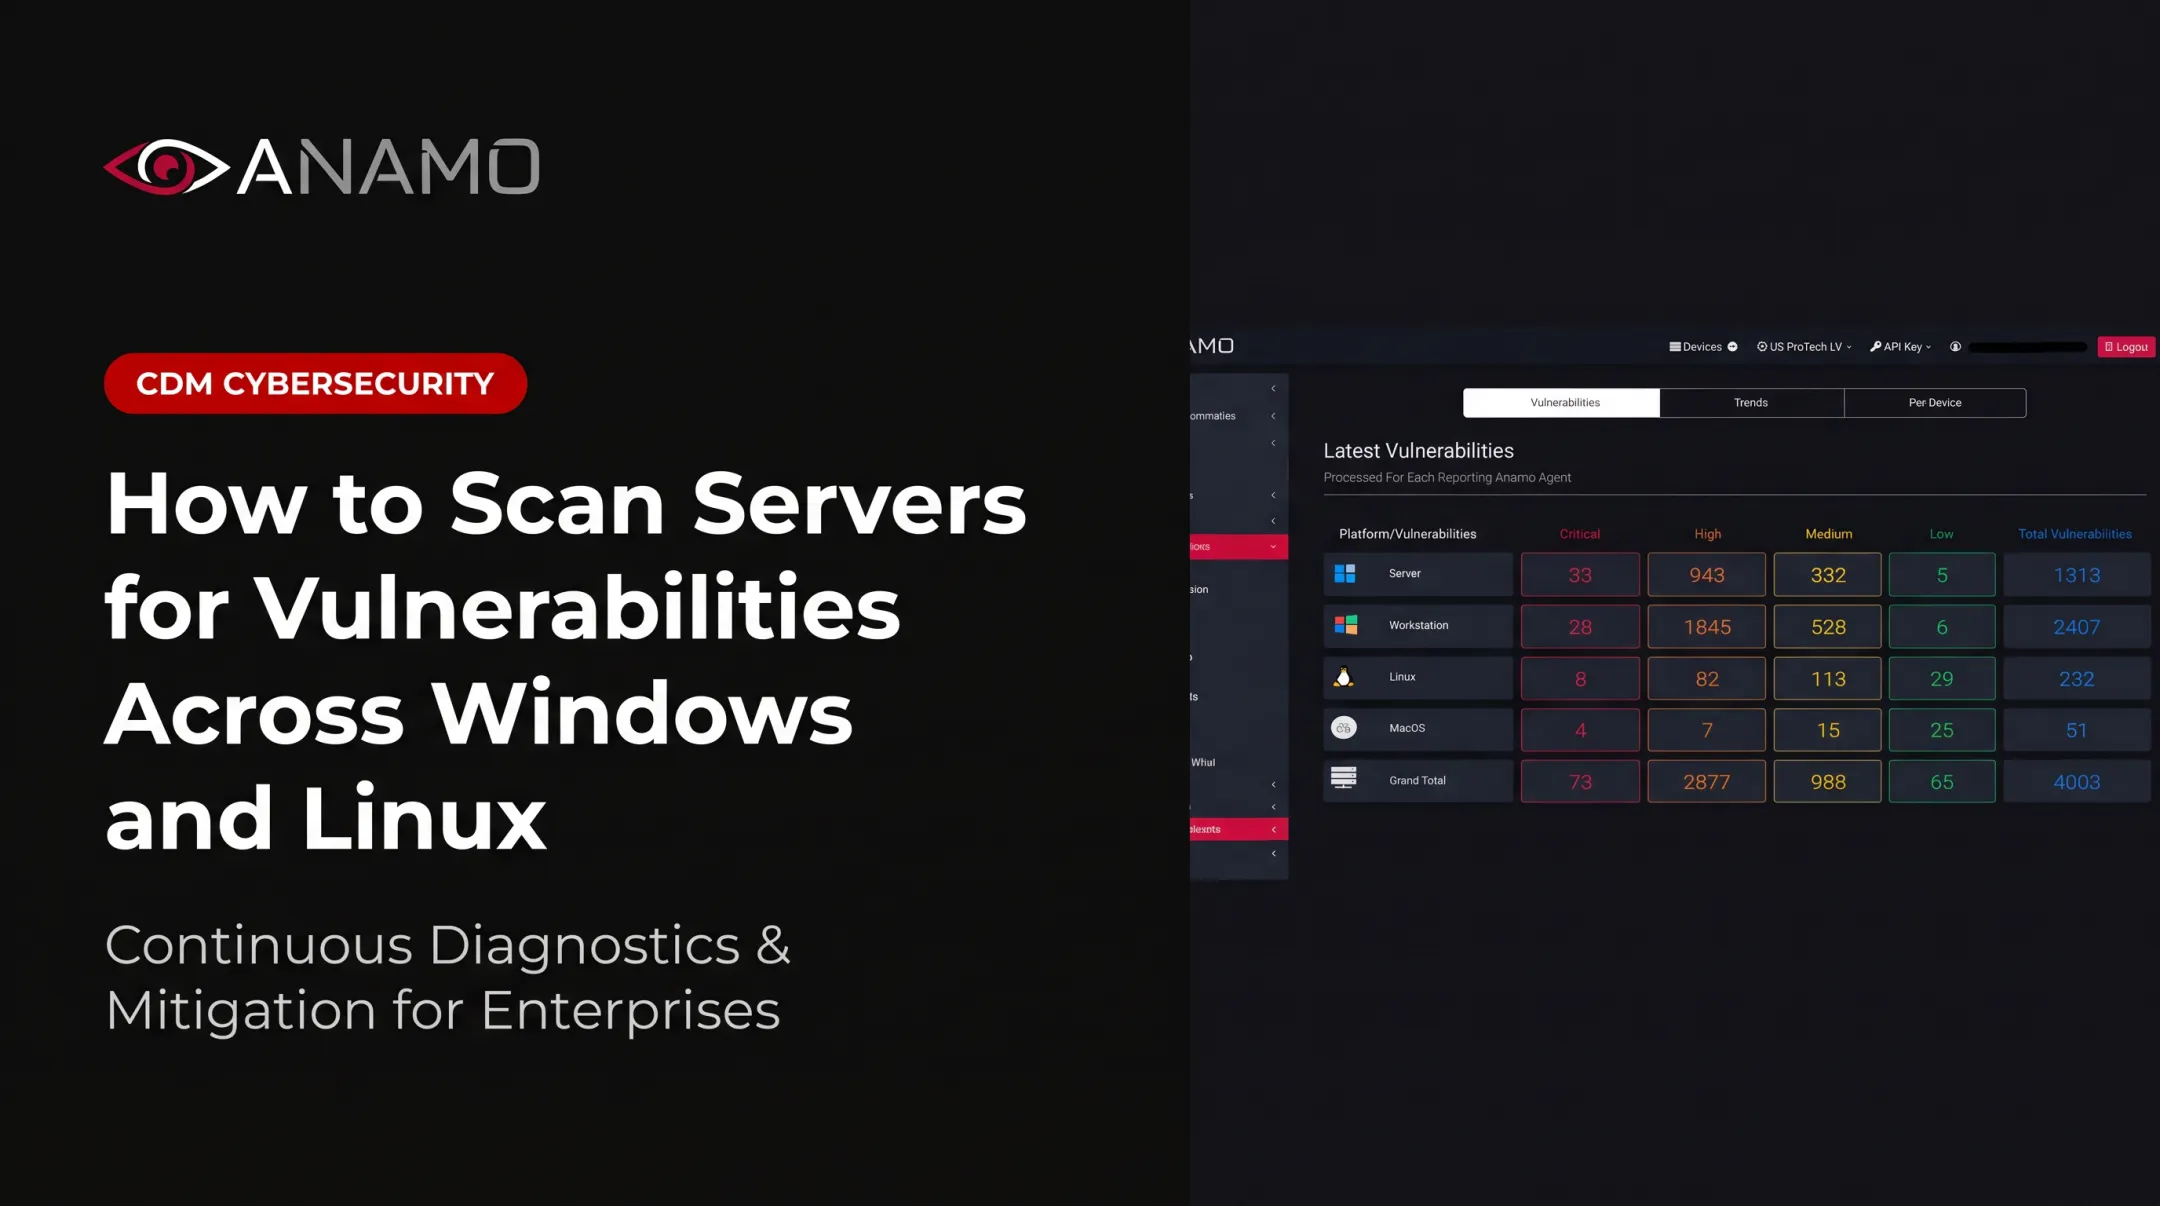
Anamo's platform, for example, autonomously captures UUIDs, host information, users, groups, ports, permissions, and software and package inventories across both operating systems without manual entry. That baseline is required before correlation can happen at scale.
Map Evidence to Vulnerabilities and Validate Findings
Correlate software, versions, and configurations against CVE records, vendor advisories, and misconfiguration benchmarks. But a CVE match is a candidate finding, not proof of exploitability. Version backports, vendor patches, and compensating controls all change the picture.
Red Hat's backporting guidance is a good illustration: fixes get backported into older package versions, so a version-only scanner can flag a patched RHEL system as vulnerable when it isn't. Validation through authenticated checks, configuration evidence, and manual review catches this before it wastes remediation hours.
The stakes of skipping validation are real. Mandiant's M-Trends 2025 documents CVE-2024-3400 in PAN-OS GlobalProtect: disclosed April 12, 2024, with proof-of-concept code public within a day, and more than a dozen separately tracked groups exploiting it within two weeks.
Common categories to watch for:
- Missing patches and unsupported software
- Insecure configurations and weak authentication
- Excessive privileges and exposed services
- Local privilege escalation and remote code execution
- Information disclosure paths
Prioritize, Remediate, and Verify
Assign ownership and separate urgent containment from standard patching. For systems that can't be patched immediately, options include segmentation, access restrictions, heightened monitoring, or documented risk acceptance.
This is where a unified platform earns its place. Anamo's CDM-SIEM approach centers on autonomous, always-on data collection, CVE and permission visibility, and dashboards that surface remediation priorities. Stated capabilities include change detection within seconds across Linux, Windows, workstations, servers, and VMs.
That support does not replace validation or governance. It sustains the reassessment cycle that manual-only processes struggle to keep up with.
Once remediation happens, confirm the fix landed on the correct asset and the vulnerability is actually gone. Then recheck cloned images, failover systems, and anything that might have missed the original window. Assets and threat conditions keep changing, so the loop starts again.
Where Vulnerability Discovery Is Applied and What Affects Results
Discovery delivers the most value in a few recurring environments:
- Corporate endpoints, remote/hybrid devices, file and application servers, identity infrastructure, and virtualization hosts
- Manufacturing and critical infrastructure settings where IT and plant-floor OT coexist
- Government contractors needing defensible evidence of inventory and continuous monitoring
- Distributed enterprises needing central visibility without losing business-unit ownership
Timing matters as much as scope. Run discovery continuously or on a recurring schedule, and trigger extra coverage when conditions change:
- After new asset deployment
- After major configuration changes
- Following a new high-risk advisory
- After an incident
- Around compliance assessments
What Affects Accuracy
| Factor | Why it matters |
|---|---|
| Coverage | Agent deployment, credentials, offline devices, segmented networks, and OT constraints all limit what's visible |
| Data quality | Duplicate records and stale software data produce false confidence |
| Method | Authenticated vs. unauthenticated, agent vs. network-based; each has blind spots |
| Operating conditions | Maintenance windows, bandwidth, and scan frequency affect both coverage and risk of disruption |
OT environments deserve particular caution. NIST's OT security guide recommends passive scanning where possible and advises extreme care with active probes, since equipment that's never been tested shouldn't be assumed safe to scan live.

Reporting should serve two audiences at once. Executives need trend summaries; practitioners need asset, weakness, evidence, owner, due date, and verification history.
Before deployment, review authorized access, telemetry privacy, data retention, and OT safety procedures.
Common Issues, Misconceptions, and When Discovery Approaches Fall Short
A few assumptions cause more damage than the vulnerabilities themselves.
"A scanner sees everything." It doesn't. Unauthorized assets, disconnected endpoints, segmented networks, and failed credentials all create blind spots a scan report won't flag as missing.
"Every CVE is equally urgent." Technical severity isn't the same as actual exposure. A critical CVSS score on an isolated, non-internet-facing system is a different priority than a medium-severity flaw on an internet-facing server handling customer data.
"A clean scan means the asset is secure." It doesn't account for unknown vulnerabilities, weak configurations, credential abuse, or supply-chain exposure sitting outside the scan's collection method.

Discovery Isn't EDR or SIEM
These tools solve different problems:
- EDR focuses on endpoint activity, detection, and response
- SIEM correlates security events and logs
- Vulnerability discovery identifies weaknesses and exposure conditions before an incident happens
Integrated workflows improve context, but none of these should substitute for the others.
Operational Failures Worth Avoiding
- Scanning without clear asset ownership, so findings sit unassigned
- Producing reports with no remediation workflow attached
- Accepting repeated false positives without tuning the assessment method
- Ignoring Linux package backports and misclassifying patched systems as vulnerable
- Closing findings without verifying the fix actually applied
Before trusting a discovery program, check it against a short list:
- Does it cover unmanaged and offline assets?
- Are findings validated before they hit a remediation queue?
- Is prioritization based on more than severity score?
- Does every finding have an owner and a due date?
- Is reassessment scheduled, not ad hoc?
Effective enterprise vulnerability discovery is a continuous cycle, not a one-time project:
- Know what exists
- Understand how it's exposed
- Validate what's real
- Prioritize what matters
- Remediate safely and verify the result
Frequently Asked Questions
How are vulnerabilities discovered?
Teams inventory assets, collect endpoint and server telemetry, and match findings to CVE records and advisories. They then validate exploitability and prioritize by exposure and business impact on a continuous cycle.
What does a vulnerability researcher do?
A vulnerability researcher finds and validates weaknesses, documents evidence, and may coordinate responsible disclosure. Enterprise vulnerability analysts instead prioritize and remediate findings across the live environment.
What are the common types of vulnerabilities?
Common types include missing patches, insecure configurations, weak authentication, excessive permissions, exposed services, and flaws such as privilege escalation or remote code execution. Risk depends on the asset, its exposure, and the data it handles.